Already-exploited Outlook flaw hands over Windows credentials
Microsoft fixes an Outlook zero-day that leaks the NTLMv2 hash when a file is opened. The real risk lies in a 1993 protocol your company still keeps switched on.
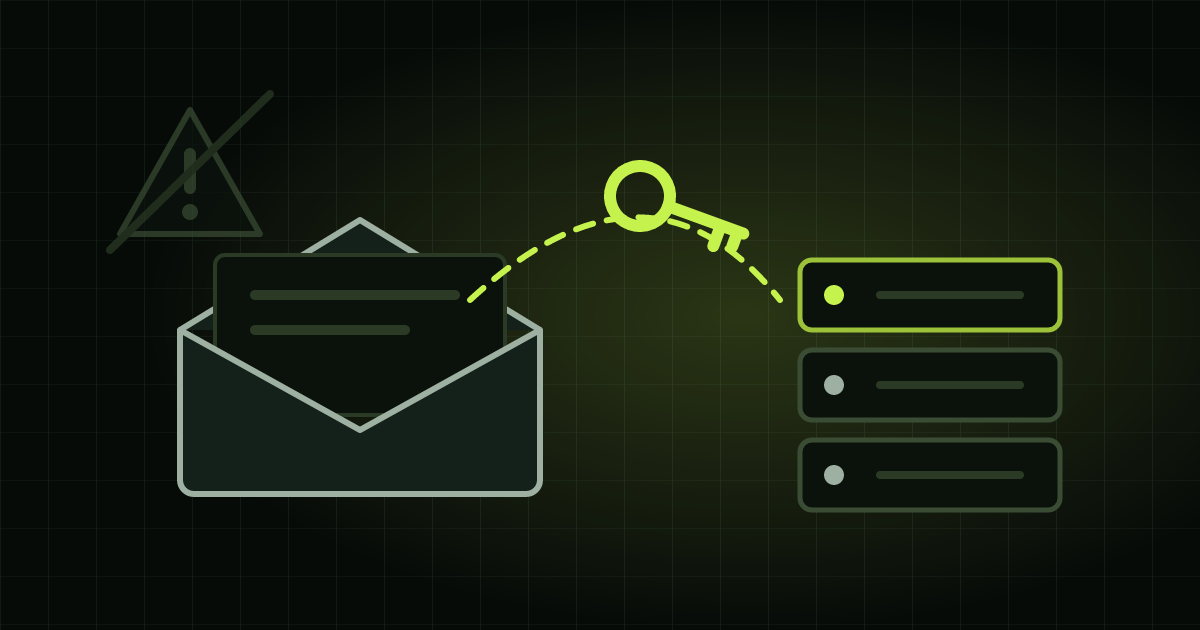
On November 10, Microsoft fixed a flaw in Outlook for Windows that criminals were already exploiting before the fix. CVE-2026-124194 makes Outlook, when opening a specially crafted message file, connect to an attacker’s server without showing the external content warning. During that connection, Windows hands over the user’s NTLMv2 hash, a code derived from the password that lets someone try to crack it or log in to other services as that person, according to Cyber Security News, the original source of this story. The score is 6.5 (moderate), but the US agency CISA added the flaw to its catalog of exploited vulnerabilities, with a November 24 deadline for federal agencies, according to Suped. Affected products are Microsoft 365 Apps, Office LTSC 2021 and Office LTSC 2024. Just viewing the message in the reading pane does not trigger the attack.
What this changes for your company
1. A moderate score isn’t a moderate risk. The flaw doesn’t install anything on its own, but it hands over the credentials of whoever opened the file. If that person has access to the ERP, finance or customer data, the attacker gets a way in. Control: require a report on how many machines with Office have already received the November update, with a deadline and someone in charge. An update without an owner becomes “later.”
2. The network lets the credential get out. The leak happens because the machine is able to talk to an outside server over port 445, used for file sharing. Microsoft recommends blocking that outbound traffic to the internet as an extra layer of protection, according to Cyber Security News. Control: ask your IT team or network vendor whether that block exists today.
3. Legacy left on is inherited risk. NTLM debuted in 1993, in Windows NT 3.1, and Microsoft put it on its list of deprecated features in 2024, according to The Register. It is still active at many companies for compatibility. Control: inventory which systems still depend on NTLM and decide who sets the date to turn it off.
In 29 years of programming, I’ve seen many incidents start with an old component that was left on “just for now.” Governance means giving that “for now” an owner and a deadline.
Originally published on IWA7 Insights, IWA7 Digital’s blog, which is now part of Escovando Bytes.